
Değerli ENKALILAR,
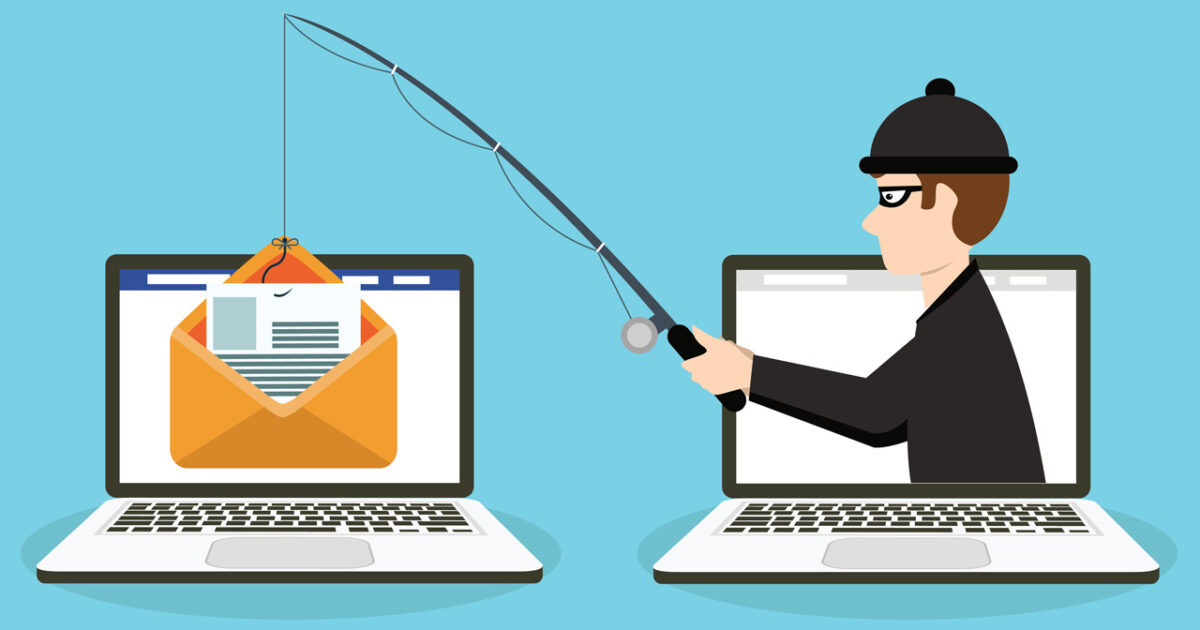
Oltalama, kullanıcının tanıdığı veya güvendiği bir kaynaktan geliyormuş gibi hazırlanmış ve kullanıcının kişisel ve hassas bilgilerini ele geçirmeyi hedefleyen bir saldırı türüdür.
Bilgi Güvenliği Ekibi olarak, Bilgi Teknolojileri Departmanı ile işbirliği içerisinde olmak üzere, e-posta oltalama yöntemini kullanarak ENKA kullanıcıları kapsamında gerçekleştirdiğimiz oltalama ve dolandırıcılık testlerine ilişkin sonuçları sizlerle paylaşmak isteriz:
E-posta içerisindeki linke tıklayan çalışan sayısı: 1.841 / 3.483 (orta risk)
Linke tıklayan ve veri girişi yapan çalışan sayısı: 63 / 1.841 (yüksek risk)
Şüpheli bir e-posta aldığınızda lütfen:
1. Hiçbir bağlantıya/linke tıklamayın,
2. Ekleri açmayın,
3. İlgili e-postayı hemen [itsupport@enka.com] adresine raporlayın.
Her internet kullanıcısının dikkat etmesi ve farkında olması gereken bu dolandırıcılık yöntemi hakkında sizler için hazırladığımız afişe aşağıdaki link yardımı ile ulaşabilirsiniz.
Dear ENKA Employees,
Phishing, is a type of attack that is prepared as if it comes from a source that the user knows or trusts and aims to capture the user’s personal and sensitive information.
We, as the Information Security Team, in cooperation with the IT Department, would like to share with you the results of phishing and fraud tests we have conducted within the scope of ENKA users, by using the email phishing method:
The number of employees who clicked on the link in the email: 97 / 3.483 (medium risk)
The number of employees who clicked on the link and entered data: 63 / 1.841 (high risk)
If you receive a suspicious email, please:
1. Do not click any links,
2. Do not open any attachments,
3. Report the email immediately to [itsupport@enka.com].
You can access the poster prepared for you about this fraud method which every internet user should be aware of.